Risk management · Reimagined

Every risk in your business.
One place. Everyone's page.

RiskEye gives you a centralised, board-grade view of the risks that matter — with visibility your team actually uses and a report you'd hand a director without editing.

Book a demo Download brochure
All systems operational
Trusted posture: SMB1001 Gold L3 CIS Controls v8 TOTP 2FA
Live · Enterprise Register
12 active
1
2
3
4
5
2
4
6
8
10
3
6
9
12
15
4
8
12
16
20
5
10
15
20
25
Low Moderate High Critical
Top risk
R-001
Ransomware · Cyber
Appetite breaches
3
vs. 5 last quarter
Coverage
78%
NIST CSF v2
SMB1001 Gold L3
SMB1001 GOLD
Level 3 · Cybercert
For SMB & mid-market
Stand up a real risk register in an afternoon.

Skip the six-figure GRC suite. Start with our 5×5 template, invite your team, and generate your first board pack the same week — with SMB1001-aligned controls out of the box.

For enterprise & boards
Group-level portfolio, without the spreadsheet chaos.

Multi-tenant by design. Cross-tenant portfolio view. Hash-chained audit trail. Snapshot reports that reproduce byte-identical for every board pack you've ever exported.

Why RiskEye

Every GRC tool promises visibility. Only one is built for the risk team.

Four opinions that shaped the product — and how they show up on day one.

Purpose-built
For risk teams, not auditors

Most GRC tools are checklists dressed up as software. RiskEye's day-job is visibility — the register, heatmap and appetite live at the top of the app, not buried five clicks deep.

Fast to start
Live register in an afternoon

No SOW. No 6-week onboarding. Import a CSV, invite your team, and generate a board-ready PDF the same day. That's the product, not a promise.

Built secure
Encryption on by default

AES-256 at rest, Fernet-encrypted 2FA secrets, hash-chained audit trail. TOTP is mandatory — not a paid upsell. See /trust for the live matrix.

Board-friendly
Reports directors actually read

Cyber-professional cover, one-page executive KPI ribbon, colour-graded coverage heatmap. Byte-identical regeneration means every snapshot is defensible.

The alternative you're using now

RiskEye vs. Spreadsheet.

If your risk register lives in Excel, SharePoint, or a shared Google Sheet, you already know it's costing you more than a license. Here's the honest side-by-side.

Capability
Spreadsheet
RiskEye
Single source of truth
No
Yes
5×5 heatmap with in-cell drill-down
No
Yes
Role-based access (default-deny)
No
Yes
Appetite breach alerts
No
Yes
Formal acceptance workflow + expiry
No
Yes
Hash-chained audit trail (SHA-256)
No
Yes
Framework coverage heatmap
No
Yes
One-click board pack (PDF · DOCX · XLSX)
No
Yes
Mandatory two-factor auth
No
Yes
Version drift & 'which tab is right?'
No
Yes
Copy-paste errors on quarter-end
No
Yes
Spreadsheets are fine when you have three risks and one owner. Past that, they cost more than they save.
The platform

A centralised place to see, track and prove your risks.

Everything a risk team needs — nothing they don't. Compliance frameworks are supported, but the day-to-day job is visibility and control.

See it
Risk Register

One board-grade register for every risk in your business — inherent, current and target scored on 5×5, with owners, appetite bands and treatment plans.

Show it
Live Visibility

Executive dashboard, appetite breach alerts and framework coverage heatmaps — so anyone can answer 'what's our top risk right now?' in under 10 seconds.

Track it
Centralised Tracking

Controls, findings, mitigations, acceptances — all linked to the risks they touch. No more spreadsheets, no more version drift.

Prove it
Hash-chained Audit

Every mutation appends a SHA-256-chained audit event. Tampering breaks the chain and is detected on export. Auditors love it.

Scale it
Multi-tenant + RBAC

Default-deny role matrix. Suspend a user or a whole tenant from the super-admin console. Cross-tenant portfolio view for the board.

Secure it
Encryption Everywhere

TLS 1.3, AES-256 at rest, bcrypt passwords, Fernet-encrypted TOTP secrets, HMAC invitation tokens. TOTP required on every sign-in.

How it works

From first sign-in to board pack — in one week.

01
Bring your risks in

Invite your team, import your existing register, or start from our 5×5 template. First risks live in under 5 minutes.

02
Connect controls & appetite

Link controls to risks, set your board-approved appetite bands, and switch on any of 7 pre-loaded framework catalogs.

03
Report to the board

Generate a snapshot PDF that reproduces byte-identical — executive cover, KPIs, heatmap and every accepted-risk with sign-off.

Customer success

"Six spreadsheets in one week. Then the board actually knew what our top risks were."

We ran risk out of six spreadsheets, three SharePoint sites and a Trello board. Half the register was six months stale before anyone noticed. RiskEye replaced the lot in a week — and it's the first time the exec team can actually see what our top 5 risks are without asking the risk manager first.

— Sarah Nguyen, Chief Risk Officer, Meridian Logistics
Meridian LogisticsFreight & warehousing · 340 staff · ASX-listed subsidiary
8 wks → 4 days
Board-pack turnaround
78 → 12
Spreadsheets retired
0 → 100%
Appetite-breach visibility
Composite case study based on typical mid-market outcomes in the first 60 days. Names anonymised at customer request.
A tour

Built for the way risk teams actually work.

Dashboard — product screenshot
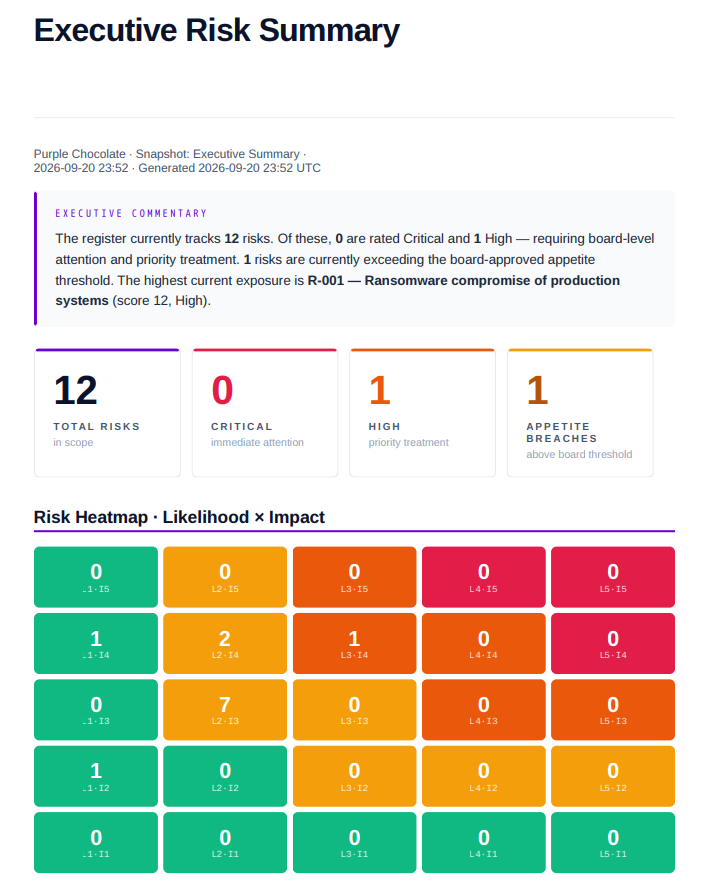
Dashboard
Executive dashboard

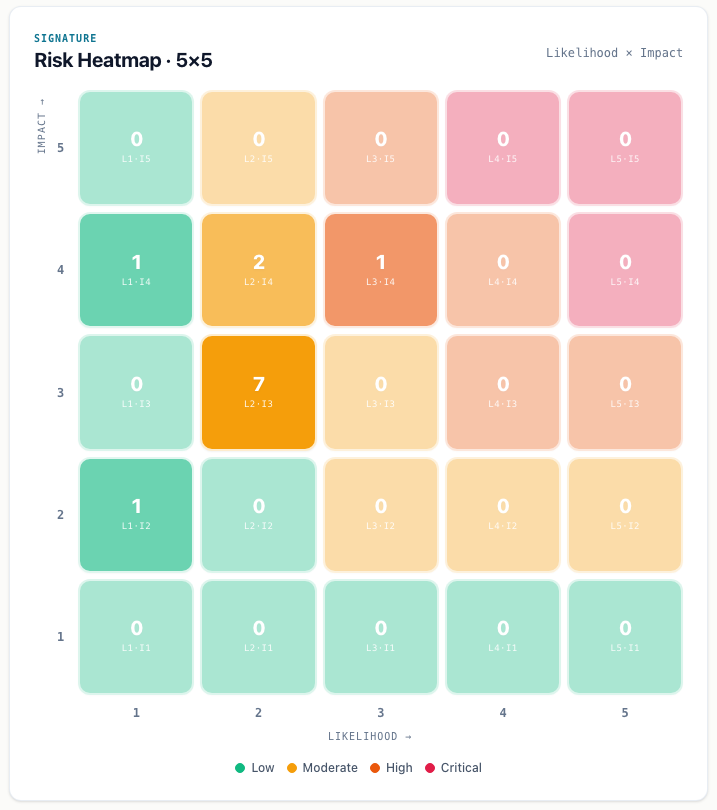
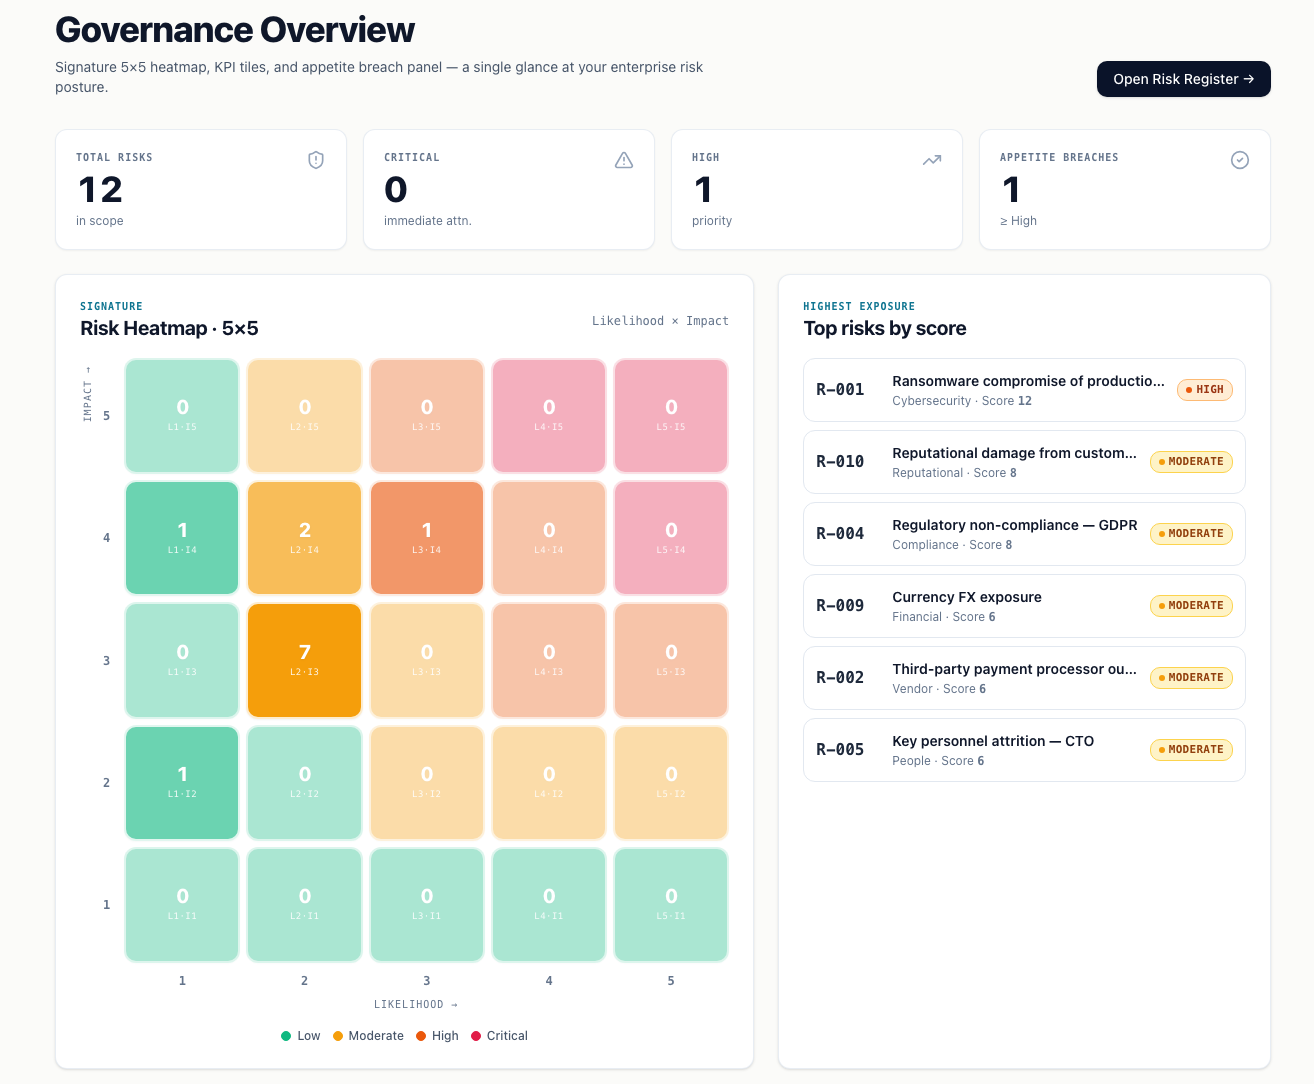
KPI tiles, appetite breach ticker, and a live 5×5 heatmap on the front page — the answer to 'what's our top risk right now?' at a glance.

Heatmap — product screenshot
Heatmap
Signature 5×5 heatmap

Every risk placed on a Likelihood × Impact grid, colour-graded by severity, with in-cell counts. Click a cell to drill down into the risks it contains.

Coverage — product screenshot
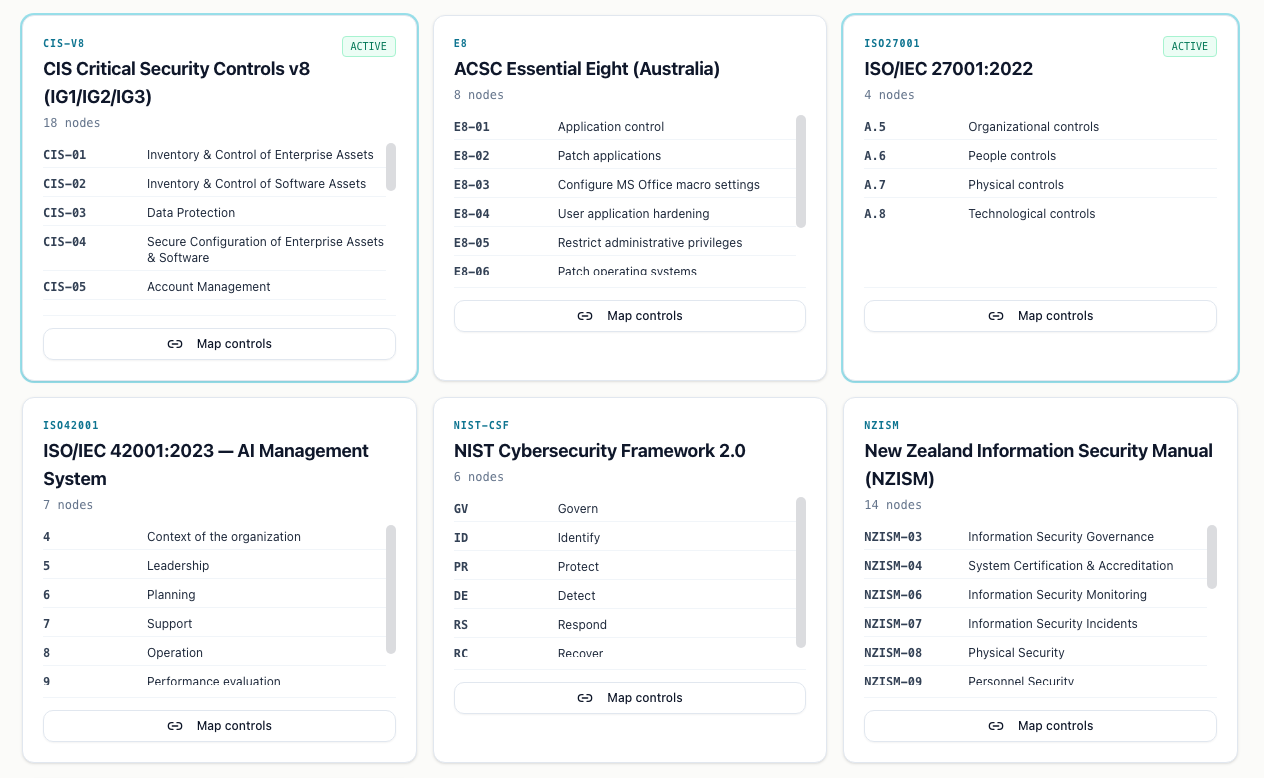
Coverage
Framework coverage

Toggle NIST CSF, ISO 27001, CIS, Essential 8, ISO 42001, NZISM or SCM0020 and see your control coverage in a colour-graded heatmap.

Reports — product screenshot
Reports
Snapshot reporting

PDF with a cybersecurity-professional cover, executive KPIs, register, accepted risks and a SHA-256 integrity hash for reproducibility.

Take it away
Download the RiskEye brochure

A 3-page PDF you can share with your board, IT committee, or budget holder — with everything on this page, cleaner.

Download PDF (RiskEye · by seQure)
Questions

Straight answers.

No — RiskEye is a risk management platform first. Framework mapping (NIST CSF, ISO 27001, CIS, Essential 8, ISO 42001, NZISM, SCM0020) is available for teams that want it, but the core job is giving you visibility over the risks in your business and a single place to track them.
See it on your own risks

A 30-minute walk-through with your data.
No slides. No sales pitch.

We'll seed a private tenant with your top 10 risks, walk you through the appetite-breach and reporting flow, and hand you super-admin keys the same day.

What's included
  • Private tenant seeded with your risks
  • Board-grade snapshot PDF the same day
  • Framework coverage across 7 catalogs
  • Super-admin keys handed over on the call